Every finding is a working exploit.
XBOW breaks into every application you expose, not just the crown jewels, and proves it. Once your team deploys the fix, XBOW re-tests it.
Top security teams trust XBOW
1,000,000,000
Chrome users affected
Google's first Chrome full-chain reward of 2026. Three bugs chained, affecting an estimated one billion users.
- Unknown bugs chained
- 3
- To a full chain
- 6 days
- Google full-chain reward
- $250K
#1
HackerOne
First autonomous system to rank #1, with 1,500+ reproducible exploits on production targets.
1st
Autonomous system
Ranked on Microsoft's MSRC leaderboard. Three critical CVEs found and proven on its own.
Security teams don't need more findings. They need proof.
Scanners and static analysis surface vulnerabilities by the thousands. Finding a flaw is not proving it's exploitable. XBOW attacks your applications and APIs the way an elite attacker does and reports only what it broke into, so your team knows what to fix first.
Proof you can act on.
Every finding comes with the working exploit, the request, the response and the steps to reproduce it. Findings in generally available classes are confirmed by a deterministic check; preview classes are labeled. Validated findings with the exploit attached, not a backlog.
Every application, not just the crown jewels.
Manual testing reaches the applications you can afford to test by hand. The rest goes untested and has fatal flaws. Point XBOW at everything you expose. A Fortune 50 organization assessed 180 applications in a month and received 1,216 validated findings.
At the speed you release. Safely.
New code ships weekly. Tests ran yearly. XBOW runs continuously or on demand and returns first validated findings in hours, so nothing ships untested between tests.
Proven in the open, against the best.
XBOW earned its record on real targets, scored by third parties, not by us. It ranked #1 on HackerOne above every human researcher. It found three critical Microsoft CVEs on its own.
In October 2026, one XBOW researcher working with agents chained three unknown Chrome bugs into a full sandbox escape in six days, and Google paid its first $250,000 full-chain reward of the year. Today, 200+ top security teams trust the same platform with their own applications.
- Stage 1
V8, Chrome's JavaScript engine
Control of memory inside the engine's sandbox.
- Stage 2
Animated-WebP image decoder
Sandbox escape. One precise write to native memory.
- Stage 3
Crashpad, the crash handler outside the sandbox
Full code execution, triggered by loading a web page.
Read how it happened: the overview on our blog, and the full exploit, stage by stage, from our research team on Labs.


XBOW attacks. Your team fixes. XBOW verifies.
XBOW: Attack.
Thousands of agents test your applications and APIs in parallel, chaining flaws into working attacks that scanners and point-in-time tests never reach.
Your team: Fix.
Each finding lands in your ticketing system with a code-specific fix suggestion and the full exploit path, so your team knows exactly what to change and why.
XBOW: Verify.
Deploy the fix, trigger a re-test, free and unlimited, and XBOW confirms it closed. No waiting for the next test window.
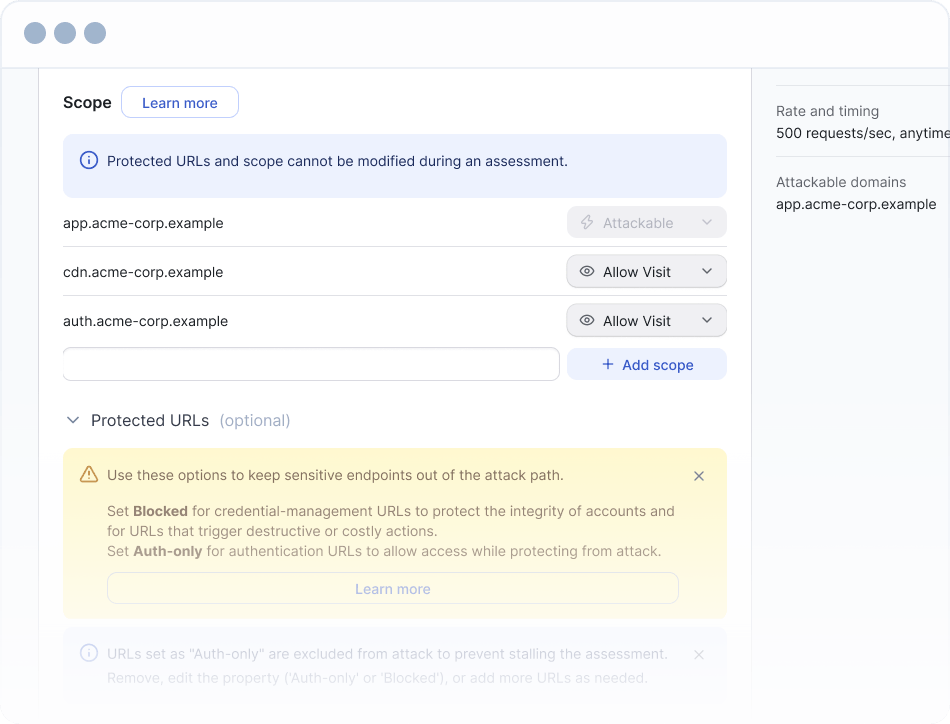
You set the rules. XBOW stays inside them.
No human drives the attack.
You set the scope, the impact level and the testing window. Every action is logged. Findings are reviewed before you see them.
Scope you control.
Define what XBOW can test. Protected URLs, rate limits and testing windows are yours to set. Pause at any time.
Safe and proven.
Production-safe checks to avoid modifying data or disrupting systems. A command checker blocks destructive actions. No model training with your data.
Observable and auditable.
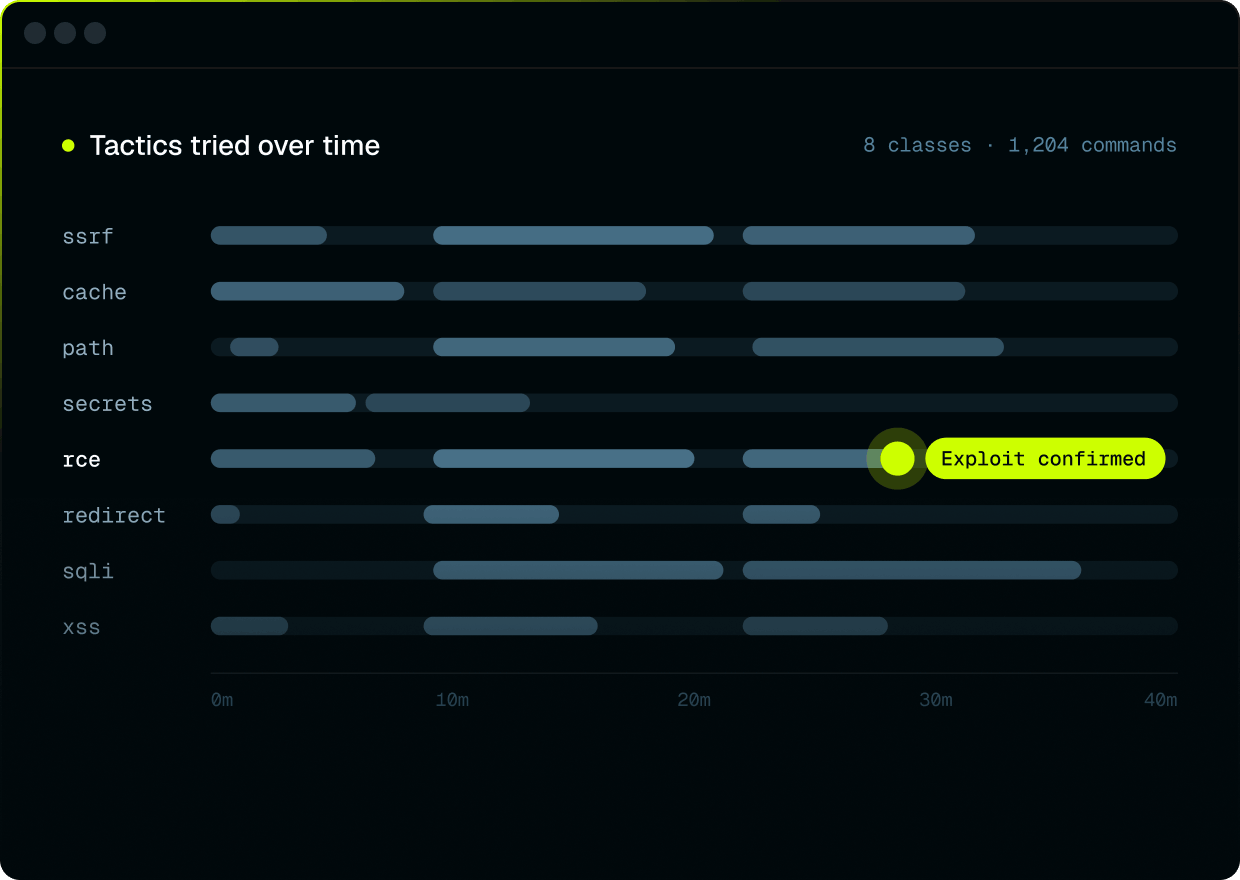
Every action is logged and reviewable. Open any finding and see the full attack path.
Deployment and compliance.
Deployment aligned to your data separation, residency and compliance requirements. SOC 2, ISO 27001, ISO 42001, PCI DSS, NIS 2.
Every finding, traced end to end.
Every XBOW finding is a complete case file: the chained attack path, the working exploit that proves it, a full log of every decision and tactic, and developer-ready remediation.
What security teams say.
See Customer Stories
“Before working with XBOW, we relied on a different pentest provider. Their findings lacked depth. Key vulnerabilities remained undetected, leaving us with a false sense of security. Additionally, while we leveraged other security tools like SAST and DAST solutions, they didn't provide the same level of real-world attack simulation that a strong pentest should deliver.”
Weimo Liu
“The best hacker on planet Earth is an AI and that AI is XBOW.”
“Before XBOW, we had a huge volume of findings which made remediation difficult. With XBOW, every finding comes with an exploit proof. That tells us exactly what to fix first.”
Farzan Karimi
“A bug bounty finding gets fixed fast because it comes verified, with proof and evidence. XBOW gives us that same value chain on our own terms, without waiting on a researcher or an alert in the middle of the night.”
Giles Douglas
“For a lean team like ours, XBOW's simplicity and flexibility were game changers. We managed setup and execution ourselves with zero friction and could trigger tests on demand whenever we needed verification. Retesting fixes was quick and seamless, a huge contrast to the delays and back-and-forth that come with traditional pentesting vendors.”
Priscilla Fong
“Every XBOW agent is a new team member.”
Leo Golovyrin